What is DNS over HTTPS? What it hides and what it doesn't
How DNS over HTTPS encrypts your lookups, what your provider and resolver can still see and how to turn it on in your browser.
DNS over HTTPS (DoH) hides your DNS lookups by sending them inside an encrypted HTTPS connection instead of as plain text. Anyone on your local network can no longer read which sites you're looking up. Neither can your internet provider unless it also runs the resolver you use. It doesn't make you anonymous though. The DNS resolver that answers your lookups, whether that's Cloudflare, Google, NextDNS or your provider's own DoH server, still sees them. And the site's IP address can still give away what you're visiting.
Below you'll see exactly what DoH hides and what it doesn't, how it compares to DNS over TLS, when it's worth turning on and how to switch it on in your browser.
What DNS over HTTPS actually does
A normal DNS lookup is one of the few parts of browsing that still travels as plain text. Your browser asks "what's the IP address for example.com" and both the question and the answer go out unencrypted. Your internet provider sees it. So does anyone running a packet sniffer on the same Wi-Fi network, one of several ways networks and sites can watch what you do online.
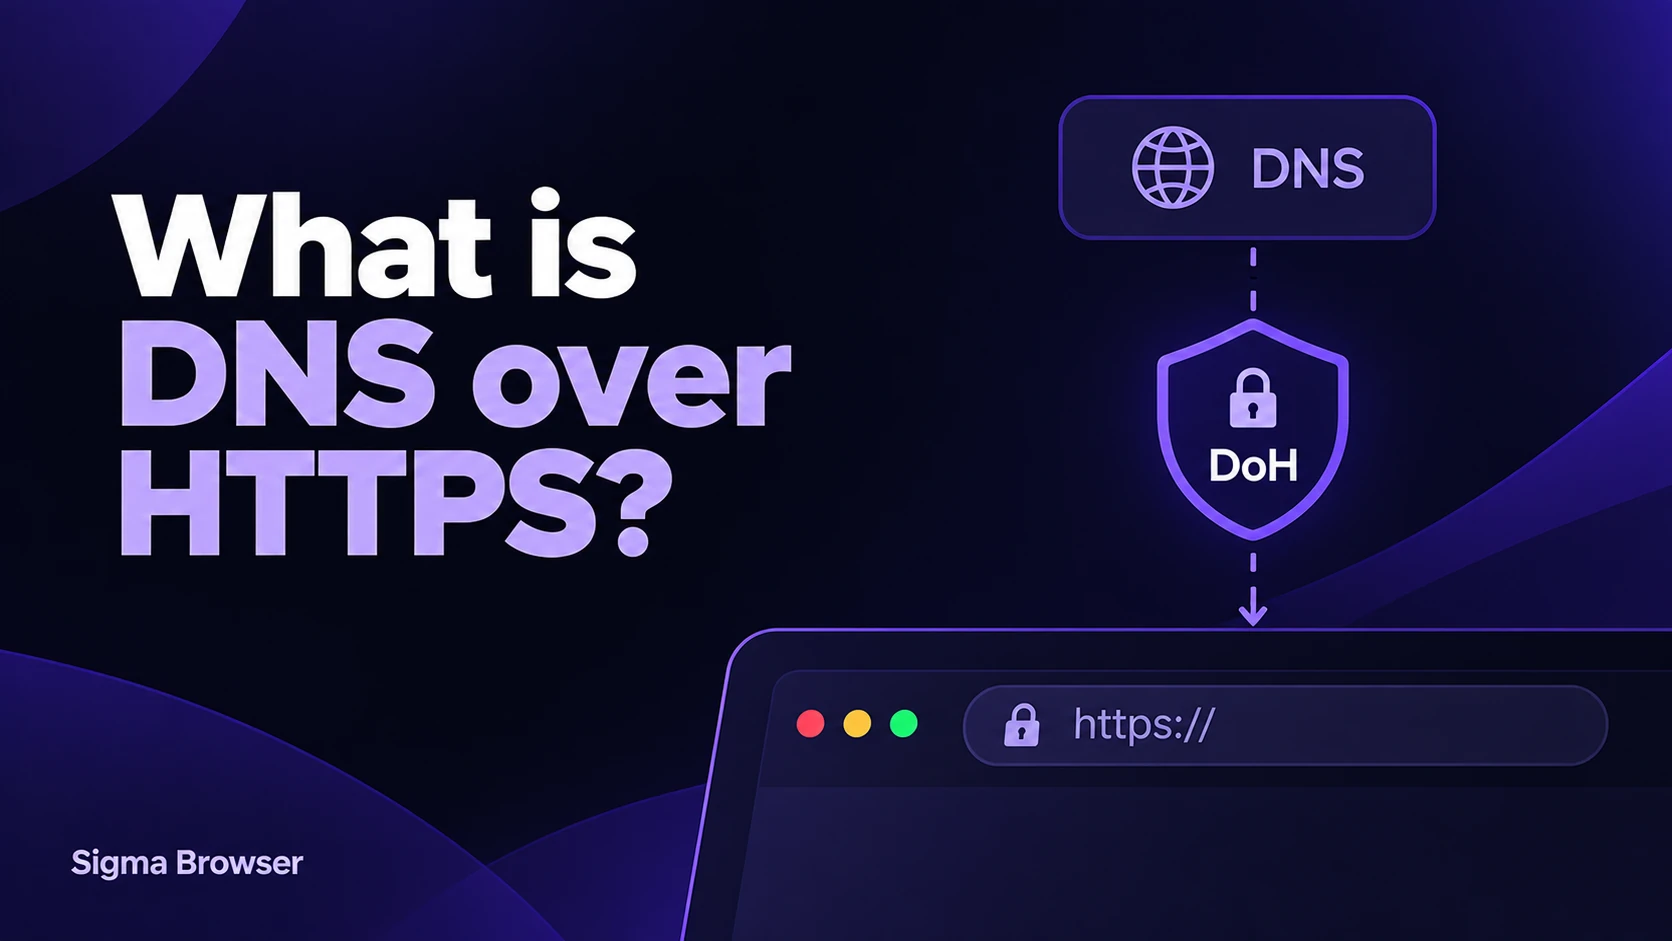
DNS over HTTPS wraps that same question inside HTTPS, the protocol that already encrypts the rest of your connection to most sites. Instead of asking a DNS server directly your browser sends the lookup to a DoH resolver over the same kind of encrypted channel it uses to load a web page. Anyone watching your network traffic sees an HTTPS connection and nothing more specific than that.
The name itself tells you what changed. It's still the same DNS lookup. HTTPS is just how the question now travels.
What DNS over HTTPS hides and what it doesn't
DoH hides your DNS lookups from your local network and from anyone between you and the resolver. It doesn't hide them from the resolver itself. It also doesn't fully hide which sites you visit.
Three things are worth separating here because people often lump them together.
The resolver still sees your queries. Turning on DoH doesn't remove the lookup. You're choosing who gets to see it. If you pick a public resolver like Cloudflare's 1.1.1.1, Google's 8.8.8.8 or NextDNS, that company sees your lookups instead of your provider. If your browser simply upgrades to your provider's own DoH server (Chrome's default behavior), your provider still sees them, just over an encrypted line. Read your resolver's privacy policy the same way you'd read a VPN's.
The site's IP address can still leak which site you're on. Once your browser has the IP address it still has to connect to it. That IP shows up in plain network traffic. Many sites share IP addresses across a CDN, which blurs this a bit. But a site on its own dedicated IP is still easy to identify even with DoH on.
The TLS handshake can leak the domain name too unless ECH is on. When your browser connects to a site over HTTPS it normally announces the domain name in plain text in a handshake field called SNI. A newer extension called Encrypted Client Hello (ECH) encrypts that field as well. Chrome and Firefox both started turning ECH on by default in 2023. Cloudflare is one of the larger hosts that supports it on the server side. But it only works when both your browser and the site's host support it. ECH is also tied to DoH. The browser fetches the site's encryption key through DNS. Mozilla says Firefox relies on DoH for ECH. That's one reason real use still lags behind support. A 2026 IFIP Networking measurement study of Firefox telemetry found that only around one in five Firefox users actually negotiated ECH on a given day between April and September 2025.
So DoH is one layer of a bigger privacy picture. On its own it stops casual snooping on DNS lookups. It doesn't replace checking who runs your resolver. And it isn't the same as hiding which sites you visit.
DNS over HTTPS vs DNS over TLS vs plain DNS
DoH and DNS over TLS (DoT) both encrypt DNS lookups. The difference is how that encrypted traffic looks to anyone watching the network. That changes where each one works best.
DoT runs on its own port (853), which makes it easy for a firewall to spot and block outright. DoH rides on port 443, the same port as ordinary web traffic. A network can't block it by port without breaking the web. Networks that want to stop it block the addresses of known DoH resolvers instead. That's a big part of why browsers went with DoH. DoT shows up more in operating systems and routers (Android's Private DNS setting is DoT, for example).
Neither one is more private at the resolver level. Whichever resolver you point either protocol at still sees your lookups in both cases.
Should you turn DNS over HTTPS on or off?
Turn it on when you're on a network you don't trust (public Wi-Fi, for example) or when you'd rather your internet provider not see which sites you look up. Keep it off on a network where DNS-level filtering does a job you actually want done.
Good reasons to turn it on:
- You connect to public Wi-Fi at cafes, airports or hotels often.
- You don't want your internet provider logging your lookups (pick a resolver that isn't your provider for this).
- Your provider's DNS is slow or unreliable and a public resolver works better for you.
Reasons to leave it off or turn it back off:
- Your network runs DNS-level parental controls or content filters you rely on. DoH can route around them.
- Your workplace uses DNS-based security filtering or internal DNS names for its tools. DoH would bypass both.
- You're troubleshooting a connection issue and want to rule out DNS as a variable.
- You've noticed slower page loads since turning it on. A resolver that's farther away or busier than your default one can add a delay to every new site you open.
Most people can leave DoH on by default and turn it off only on networks where they specifically want local DNS control back.
DNS over HTTPS vs a VPN
DoH encrypts only your DNS lookups. A VPN encrypts everything leaving your device and routes it through a server that masks your IP address too. If you don't want your provider to see which sites or even which IP addresses you connect to, DoH alone won't get you there. That's a VPN's job. With a VPN your provider sees only that you're connected to the VPN server. So treat the two as complementary rather than interchangeable. Atomic VPN is one option that encrypts the whole connection rather than just DNS.
How to turn on DNS over HTTPS in your browser
Most major browsers have had DoH for years now. Turning it on usually takes under a minute.
Chrome. Go to Settings > Privacy and security > Security and find "Use secure DNS" under Advanced. By default Chrome uses your current provider's DoH server if it has one. To send lookups somewhere else choose a provider from the list or enter a custom one.
Firefox. Go to Settings > Privacy & Security and scroll to the DNS over HTTPS section. Pick Increased Protection. Choose Max Protection instead if you want Firefox to warn you rather than quietly fall back to plain DNS. Then choose a provider or enter your own.
Edge. Open Settings, go to the privacy and services page, find the Security section and turn on "Use secure DNS." It works the same way as in Chrome since Edge also runs on Chromium.
Safari. Safari doesn't have its own DoH switch. On macOS 11 or later (and iOS 14 or later on iPhone) you turn on encrypted DNS for the whole device instead. Download a DNS configuration profile from your chosen resolver. Then approve and install it in System Settings (Settings on iPhone). After that Safari and most other apps use it automatically.
[IMAGE: Chrome Use secure DNS screenshot, alt="Chrome's Use secure DNS setting under Privacy and security"]
How to check it's actually working
After turning it on check that the browser really uses it and isn't quietly falling back to plain DNS. Firefox shows a status next to the setting: Active, Not active or Off. Chrome and Edge don't show a status. Use an outside check instead. With Cloudflare as your resolver open 1.1.1.1/help and look at the "Using DNS over HTTPS (DoH)" line. For any resolver a DNS leak test site shows which servers actually answer your lookups.
If the test shows your provider's servers even though you picked another resolver, the setting didn't take. Often the network blocks DoH or a work or school policy turns it off. If you left Chrome on its default setting, seeing your provider there is normal. Chrome upgrades to your provider's own DoH server.
Encrypted DNS is usually one piece of a bigger privacy checklist. See how the major options compare on the most private browsers of 2026 if you're picking a browser around privacy specifically.
Encrypted DNS in Sigma
Sigma is a free private browser built on Chromium. DNS over HTTPS is part of how it connects, along with TLS 1.3 and HTTPS.
Encrypted DNS covers only the lookup. So Sigma adds protection for the rest of the visit: a built-in ad blocker, real-time warnings about phishing sites and Private Profiles that keep work, personal and other accounts apart. Profile data is encrypted and secured by a 12-word recovery phrase.
Download Sigma for free on Mac, Windows or iPhone.
More articles
Download Sigma Browser
Questions & Answers
reach out to us on X at @Sigma_Browser
Get Sigma on Android


